 3AM Marketer
Tampered Claude Code Extension Hit Up to 5,000 Cursor Users
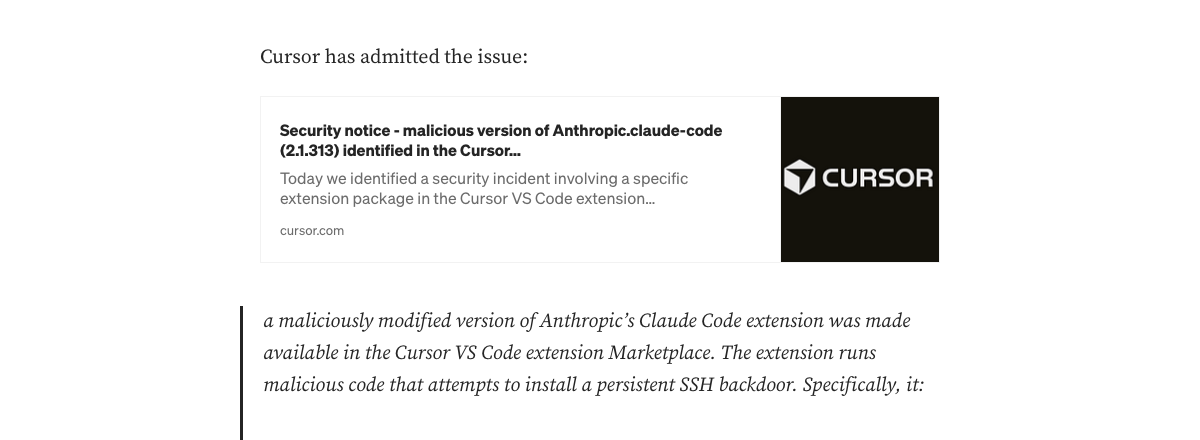
A compromised Claude Code extension on the Cursor marketplace exposed 5,000 developer workstations to SSH backdoors and data harvesting on October 29, 2026.
Cursor reported that around 5,000 developer systems were impacted after an auto-updated version of Anthropic's Claude Code extension planted a remote access backdoor on October 29, 2026.124
Network IOCs and the svc-telemetry key
The malicious payload communicates via HTTP POST requests to a beacon located at 134[.]209[.]82[.]225:8099/beacon. It then attempts to establish a persistent reverse SSH tunnel to 134[.]209[.]82[.]225 on port 22.1
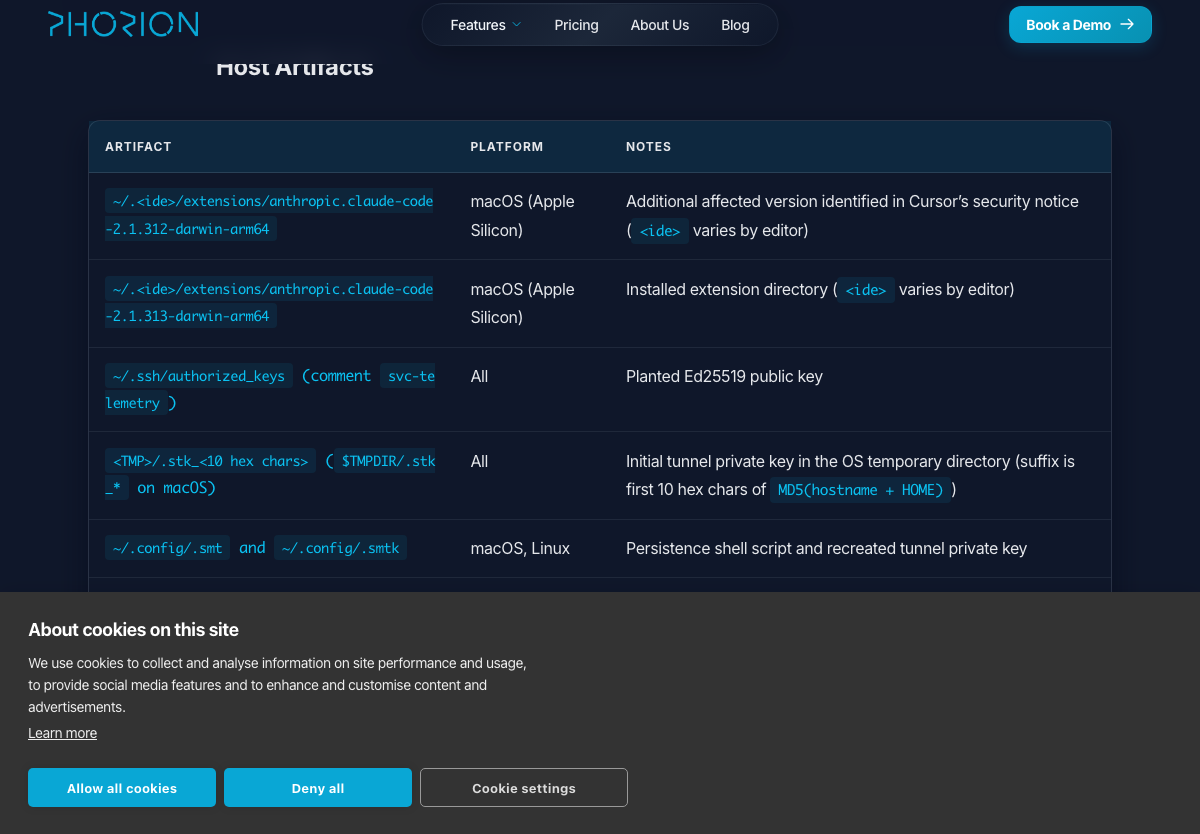
During execution, the malware gathers developer data including hostname, username, OS, architecture, home directory path, environment variable names, working directories, configured Git email, and public IP. To enable inbound SSH access, the code appends an attacker-controlled Ed25519 public key labeled with the comment 'svc-telemetry' into the user's ~/.ssh/authorized_keys file, setting restrictive directory and file permissions.13
LaunchAgent and SysMon persistence mechanics
The extension installs platform-specific persistence mechanisms across macOS, Linux and Windows developer workstations. On macOS endpoints, the malware deploys a LaunchAgent configured at ~/Library/LaunchAgents/com.apple.sysmond.plist. On Windows machines, the installer registers a scheduled task named 'SysMon' designed to execute with SYSTEM privileges, alongside a fallback script named sysmon.cmd placed directly inside the user's Startup folder.2
The backdoor attempts to enable macOS remote login through the systemsetup command. However, because it runs under standard user permissions, systemsetup prints an administrator-access error and exits without turning on the local SSH daemon.3
Incident response and remediation checklist
First, inspect ~/.ssh/authorized_keys and purge any public key entry ending with the 'svc-telemetry' comment. Second, terminate network traffic directed to 134[.]209[.]82[.]225 on port 22 and port 8099. Third, kill any running ssh or autossh tunnel to that address, then remove ~/Library/LaunchAgents/com.apple.sysmond.plist on macOS, the @reboot cron entry on Linux, or the SysMon scheduled task and sysmon.cmd Startup script on Windows, along with the hidden ~/.config/.smt and ~/.config/.smtk files on macOS and Linux. Finally, verify that Claude Code in Cursor is updated to replace the compromised release, and rotate all environment variables exposed on affected endpoints.123